EU compliance
in Medusa
The EU rules a store cannot skip, in one plugin: GPSR product safety, RODO / GDPR consent and data subject requests, and the Omnibus price transparency rule. One panel in the admin, a small store API for the storefront, and demo mode with sample data.
What exactly
this integration does
-
GPSR without another tool
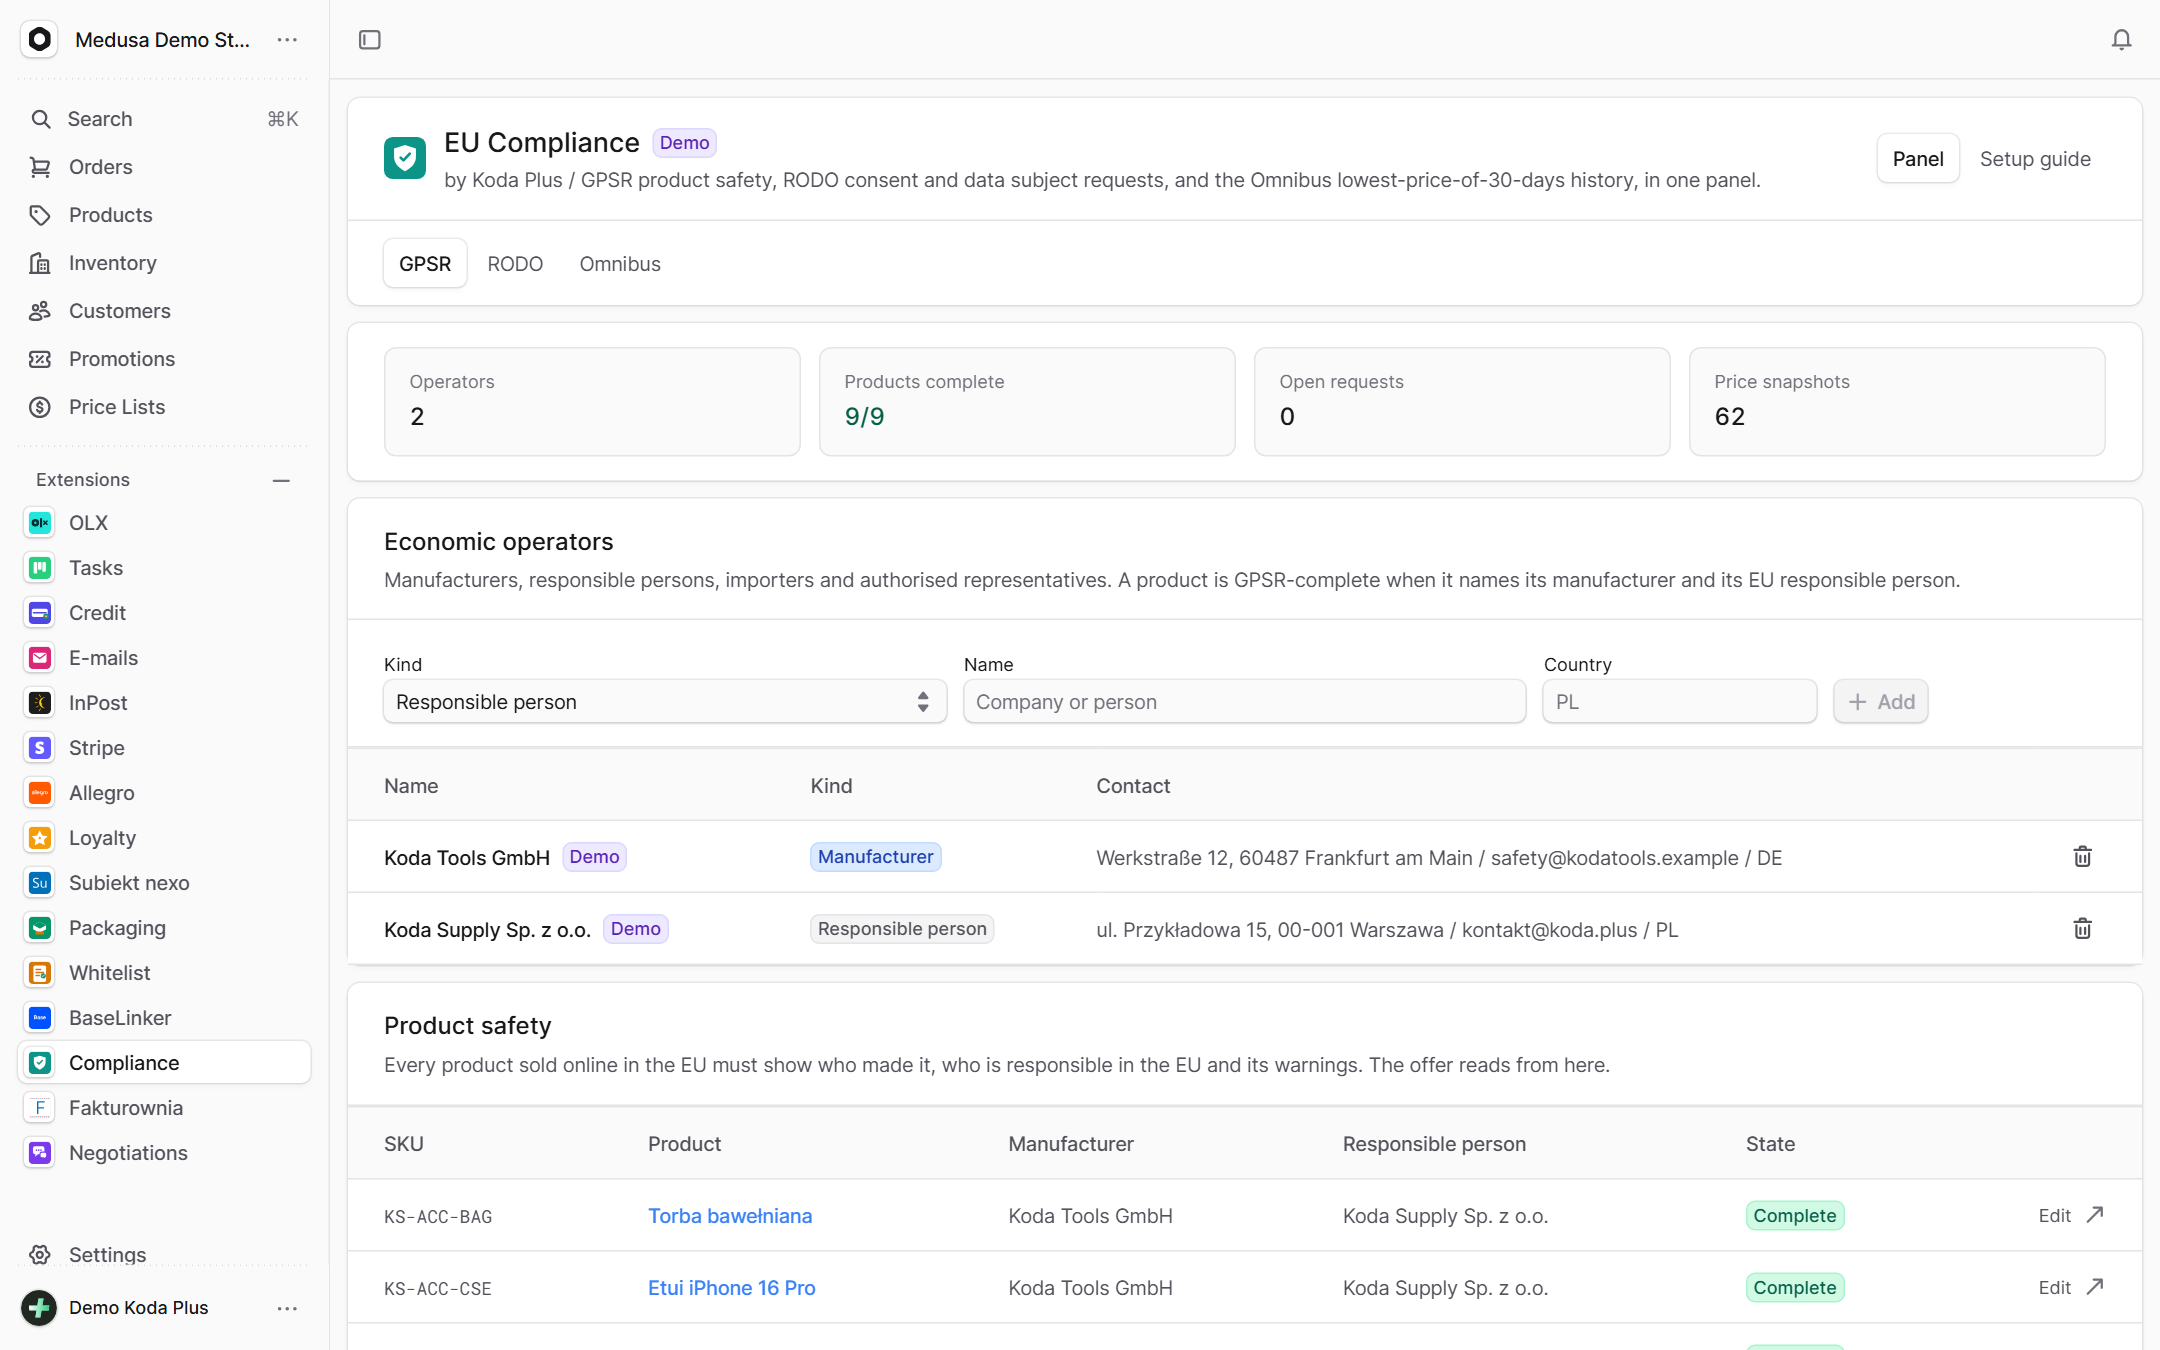
Manufacturers and EU responsible persons, a safety record per product (who made it, who is responsible, warnings and safety information) and the completeness check the distance-sales offer reads from.
-
RODO: consents and requests
Consent records from the cookie banner, the account and the checkout, and a data subject request queue (access, erasure, portability, objection) worked by the team in the admin.
-
Omnibus from snapshots
A daily snapshot of the catalog's base prices, because Medusa keeps no price history – the snapshots are the history. A reduction has to show the lowest price of the last 30 days, and it does.
-
Complete in green or red
A product is GPSR-complete when it names its manufacturer and its EU responsible person. The panel shows the state of every product and counts the incomplete ones.
-
A store API
A public read of an offer's safety info and a SKU's price window, a consent recorded before login, and requests or the company's own status only for a logged-in customer.
-
The contract in the host admin
koda.integration/1: a compliance line on the product and customer pages and counters for incomplete records and open requests.
How it guards
your data
-
Sections you can switch off
GPSR, RODO and Omnibus are enabled separately in the options. What you do not use, the admin does not show.
-
Demo only on request
Sample operators, records and price history are flagged demo, turned on only by demo: true – never by a missing key.
-
Requests behind a login
A customer files a request about their data only from their own account, and the admin links it to the customer. Public routes only read or record a consent.
Setup
in three steps
The full list of options, events and API routes is in the package README on GitHub.
Paste it into Claude Code, Cursor or another AI assistant in your Medusa project: it installs and configures the integration, with writes off.
- 1 Install the package from npm.
npm install @koda-plus/medusa-plugin-compliance - 2 Add the plugin to medusa-config.ts.
plugins: [ { resolve: "@koda-plus/medusa-plugin-compliance", options: { // Everything is optional. demo: process.env.COMPLIANCE_DEMO === "true", sections: ["gpsr", "rodo", "omnibus"], consentPurposes: ["functional", "analytics", "marketing"], }, }, ] - 3 Run the migrations and open the integration in the Medusa admin.
npx medusa db:migrate
Running for our clients
See our portfolio
 biolcheck


Other
integrations
- Allegro Offers, orders, stock and parcels
- BaseLinker Cards, stock, prices and orders both ways
- Subiekt nexo Orders as ZK, WZ and invoices with KSeF
- Fakturownia Invoices, corrections and KSeF exactly once
- InPost Parcel lockers, courier and COD on ShipX
- OLX Adverts that match the store's stock
- Stripe Volume, fees, disputes and account health
- Negotiations Target price, counter offer, acceptance
- Trade credit Limits, terms and customer balances
- Loyalty Points, a reward ladder and a ledger
- Packaging Piece, box, pallet, minimum and step
- VAT whitelist NIP, VIES and REGON in one panel
- E-mails Ready templates in Polish and English
- Tasks Tasks on orders, products and customers
Tell us about your project,
we'll tailor the rest to you
A 15-minute call is enough for us to know whether we are a fit for your project.
We start from what you need, not from an off-the-shelf solution.